

Map requirements to controls
Connect obligations to the policies, controls, risks, and business processes that satisfy them.
Audit prep shouldn't mean reconciling risk and compliance in two different systems
Manage compliance across the standards and regulations that matter to your organization.
Map requirements to controls, identify gaps, reuse evidence across programs, assign remediation work, and use AI to continuously manage your compliance program.
Popular frameworks & regulations
AI-assisted identification
Comprehensive mapping
Automated collection
Real-time tracking
One connected workflow
From requirements to reporting
Trusted by organizations across 55 countries and 21 industries
Cross-framework compliance
Connect controls and evidence to multiple standards and regulations. Tracker makes overlapping requirements visible so your team can reuse good work without losing the context each program requires.
Control
Third-party risk assessment
Standards, frameworks & regulations
Tracker gives each program its own structure while connecting shared controls, evidence, risks, and remediation across the library.
standard
Connect information security requirements to controls, evidence, gaps, owners, and remediation work in one continuously managed program.
Explore ISO 27001framework
Organize outcomes across Govern, Identify, Protect, Detect, Respond, and Recover, then connect them to controls, evidence, risks, and action plans.
Explore NIST CSF 2.0attestation
Manage Trust Services Criteria, control ownership, recurring evidence, exceptions, and remediation without separating audit readiness from risk.
Explore SOC 2standard
Manage AI policies, risks, controls, evidence, impact assessments, and improvement work against ISO 42001.
Explore ISO 42001regulation
Organize regulatory obligations by AI system, map them to controls and evidence, surface gaps, and coordinate accountable remediation.
Explore EU AI Actframework
Connect AI governance and compliance activities with the Govern, Map, Measure, and Manage approach to AI risk management.
Explore NIST AI RMFCross-framework use case
Map your existing ISO 27001 controls against NIS2 requirements. Tracker distinguishes existing coverage from partial coverage and gaps, then helps your team manage the work that remains.
Explore NIS2 complianceExisting program
ISO 27001 controls
AI governance
Build an AI governance program around the outcome you need, then connect work across ISO 42001 and the EU AI Act.
Inside Essential Compliance
Connect obligations to the policies, controls, risks, and business processes that satisfy them.
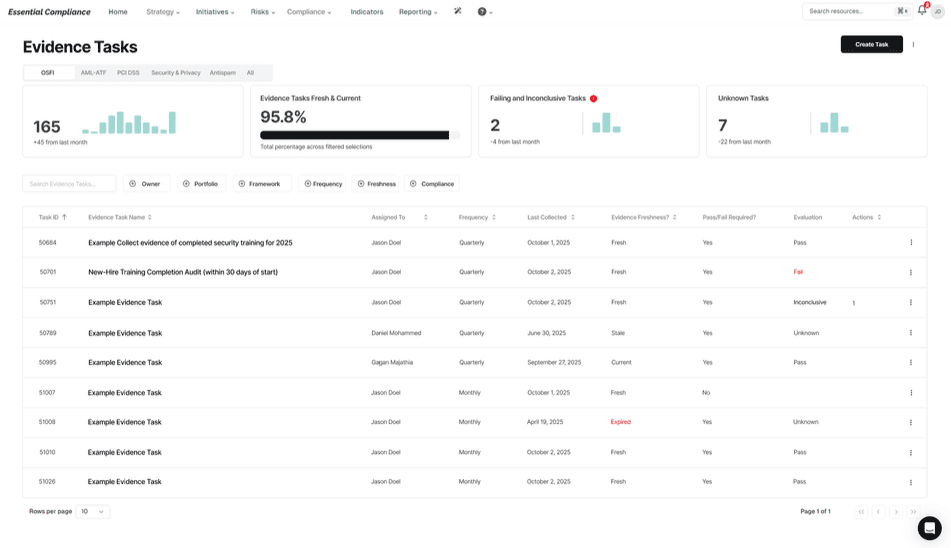
Assign recurring evidence tasks, monitor freshness, and preserve an audit-ready history.
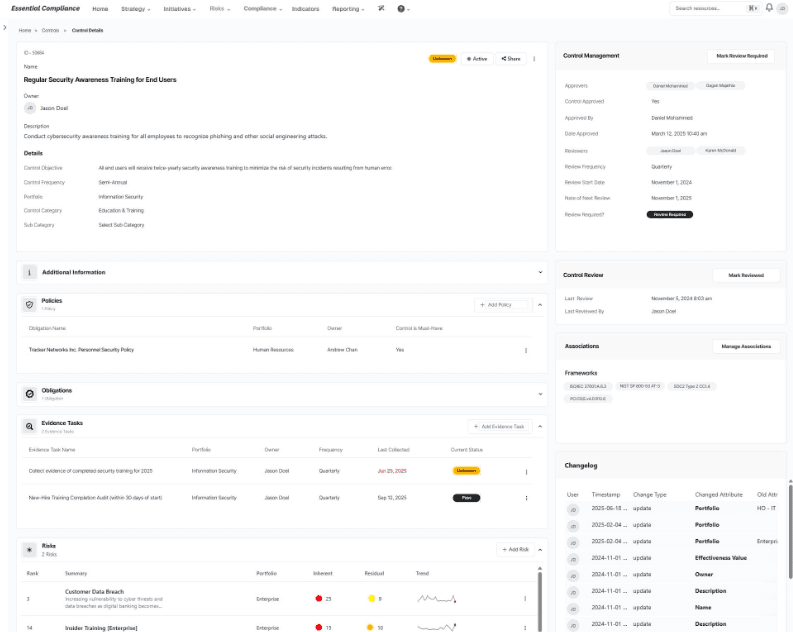
Give remediation work an owner, due date, status, and direct link back to the requirement.
Essential Compliance
Trusted by customers and rated highly across all categories


